Last Updated on 9 October, 2026
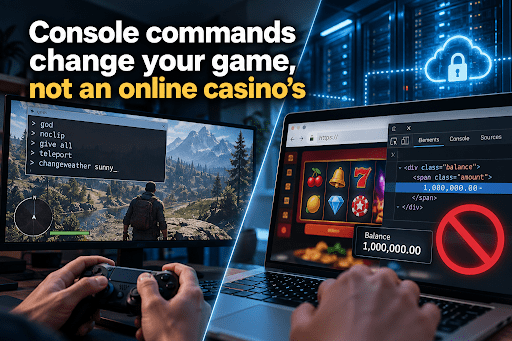
A command typed into a game console can sometimes change the weather, load another area or modify a character’s inventory. Open the developer tools in a browser, however, and the same idea stops working in the way many “casino hack” videos imply.
The difference is not the command itself. It is where the authoritative version of the game state exists.
In a single-player title, important information may live on the same machine as the player. In a remote gambling system, the browser mainly presents information supplied by systems running elsewhere. Understanding that boundary explains why a local configuration change can reshape one game while leaving an online casino account untouched.
Why console commands can change a game on your computer
A developer console is an interface intentionally connected to a game engine. When a command changes a map, variable or object, the software has been designed to recognize that instruction and the user has the required permission to run it.
The same principle applies to configuration files. A locally stored setting might control graphics, controls, physics or another part of the software because the application reads that file as part of its own state.
None of this gives a console universal authority over other software. The command works because the program receiving it has explicitly exposed that function.
Where that authority ends at an online casino
That distinction becomes important when moving from a local game to an online casino canada service. ToonieBet, for example, operates an international platform for people in Canada outside Ontario under Tobix Limited and states that it is licensed by the Tobique Gaming Commission under licence No. 0000050.
The browser in this environment is only one component of a larger system. An authenticated request travels from the user’s device to remote infrastructure, where the platform can check the account, session, permitted transaction and available funds before processing the event.
The authoritative records therefore sit beyond the web page itself. The server maintains the transaction history and account state, while the browser receives information and renders it on screen. That architecture is fundamentally different from a single-player program whose meaningful state can be stored and changed locally.
Anyone using gambling services in Canada should participate only if they have reached the legal gambling age applicable in their province or territory. Provincial responsible-gambling and self-exclusion services are available when gambling becomes difficult to control.
A changed screen is not a changed transaction
Browser developer tools are powerful, but their power is easy to misunderstand.
A user can edit HTML, alter CSS, hide an element or replace text already displayed in a tab. A balance reading “10.00” could therefore be made to display “1,000,000.00.” The browser may show the altered number convincingly, but no corresponding financial event has taken place.
Mozilla’s documentation notes that live HTML edits made through developer tools are not saved to the underlying website. In a server-authoritative system, changing what the browser displays does not create a wager record, settle a transaction or rewrite the account ledger.
Local JavaScript variables fall into a similar category. They may change an animation or interface behaviour, but the remote system can independently validate whatever data eventually reaches it.
What happens between clicking and seeing a result
The important part of an online transaction happens between the initial interaction and the information returned to the screen.
At a high level, the client sends an authenticated request. The backend checks account and session state, verifies the relevant conditions and processes the transaction. The gaming system then determines and records the outcome before returning information for the browser to display.
Remote gambling standards are specifically designed around this separation. Ontario’s internet-gaming standards require critical functions, including outcome generation, to operate independently of the end-player device. Technical testing standards follow the same principle by keeping outcome logic away from the player application.
That means changing a visible number, a CSS property or a local variable does not move backward through the system and rewrite the server’s record.
When a “console trick” becomes a security issue
None of this means networked software can never contain a flaw. Poorly implemented, compromised or fraudulent platforms can have security weaknesses.
That is a different issue.
If a remote system improperly trusts data supplied by a client, exploiting that weakness would amount to interfering with a protected system rather than using an ordinary console feature. Another risk could be malicious instructions telling users to paste unfamiliar JavaScript into browser developer tools. Such self-XSS techniques can expose account information or allow code to act inside an authenticated session.
The useful distinction is therefore not simply between “commands that work” and “commands that do not.” It is between software deliberately granting local control and a remote service retaining authority over its own records.
A console can change a game when the game was built to accept the instruction. A browser can change what appears in a tab. Neither fact, by itself, changes what an online casino’s server has actually recorded.

Leave a Reply